Atlanta, Georgia · Open to remote roles

Hana
Chanyalew

Manual QA Tester · ISTQB CTFL

Thoughtful testing for software people can count on. I bring a curious eye to SaaS workflows, security platforms, and every detail in between.

Manual testing  ·  EDR security  ·  Cross-browser QA

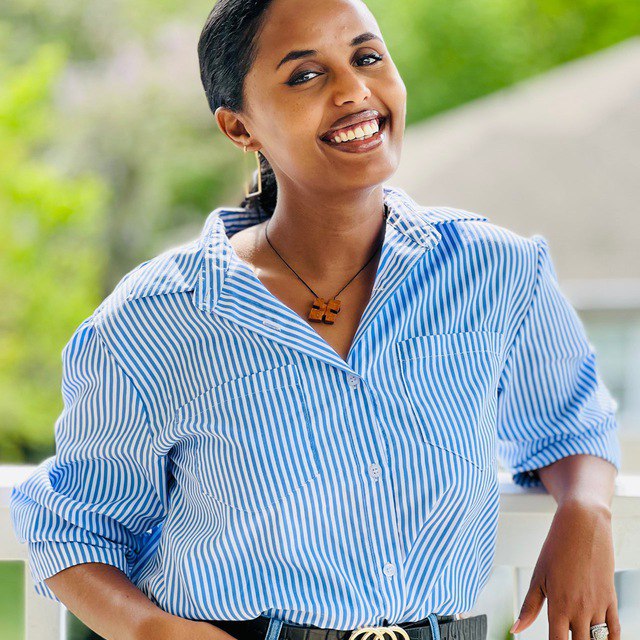
Hana Chanyalew smiling outdoors
Thoughtful testing. Better experiences.
At a glance
200+Bugs documented
50+Test cases written
5Platforms tested
01About Hana

Quality is never
an accident.

Curious by nature, methodical by practice—and always looking for the reason behind the result.

I want to understand why something breaks—not just that it does.

I’m a Manual QA Tester in Atlanta, GA, with experience spanning SaaS technical support, security platform testing, and cross-browser quality assurance. Years of solving customer problems taught me to listen closely, follow the evidence, and look for the edge cases other people might miss.

At VelocityEHS, I worked directly with Fortune 1000 clients to replicate and escalate issues across more than 10 ESG and EHS web applications. At eSafe Ethiopia, I brought that real-world perspective into structured testing—writing test cases, running regression suites, and validating threat detection on a live EDR platform.

I’m ISTQB CTFL certified, AWS cloud-aware, and comfortable validating APIs in Postman, verifying data with SQL, and checking experiences across desktop and mobile. I believe the best QA is curious, methodical, and genuinely invested in the product.
02Selected work

Clear process.
Useful findings.

A few examples of how I approach quality—from security-sensitive response flows to the small interface details that shape everyday product experiences.

Test case library01

Testing the EDR incident lifecycle

Test cases for Jegna Cyber Labs’ EDR platform, covering detection, alert triage, incident handling, and response. Each case documents actionable steps and an observable expected result.

Threat detectionRegressionIncident response
Defect documentation02

From a symptom to a reproducible bug

Reproduction steps, environment details, expected versus actual behavior, and impact—so teams can understand the issue and act on it with confidence.

JiraSeverity & impactPostman
Cross-browser QA03

One storefront, five real-world setups

BrowserStack testing for a mock shopping app across desktop browsers and iPhones, with attention to checkout flow, layout behavior, and mobile usability.

BrowserStack LiveDesktop & mobileVisual QA
Data & API validation04

Verifying what happens behind the UI

API checks in Postman and backend data verification with SQL help distinguish a presentation issue from a deeper application or data problem.

PostmanSQLRoot-cause thinking
03Test case library

Testing the details
that matter.

EDR incident lifecycle scenarios with clear steps and observable outcomes. A sample of the test cases I wrote for Jegna Cyber Labs.

EDR incident lifecycle

Five representative scenarios · Jegna Cyber Labs

TC-EDR-010

Malware detection → alert creation

Verify a new alert appears with threat type, timestamp, affected endpoint, and an unassigned status after a detection event.

Critical
TC-EDR-011

Alert assignment workflow

Confirm analyst assignment updates the alert, displays the assigned analyst, and records the change in the activity log.

High
TC-EDR-013

Merge related alerts into an incident

Validate that selected alerts are linked to a newly created incident and no longer remain as separate active queue items.

Critical
TC-EDR-024

Run a playbook on an incident

Check that automated response actions run in order and that each outcome is recorded in the incident activity trail.

Critical
TC-EDR-051

Endpoint isolation

Verify an isolation action updates endpoint status and is recorded in both response and activity views.

Critical

Defect report samples

Reproducible issues with clear user and product impact

BUG-EDR-042Critical

Alert queue does not refresh after threat detection

Expected

A new alert appears in the queue shortly after a detection event, without a manual refresh.

Observed

The alert remains hidden until the analyst reloads the page, delaying live threat triage.

BUG-EDR-058High

Incident type filter includes unrelated results

Expected

Filtering by “Spyware” shows only incidents classified with that type.

Observed

Network incidents also appear, despite the stored incident type being correct in the database.

04Cross-browser testing

One experience,
many real-world screens.

BrowserStack checks across desktop browsers and iPhones, focused on shopping, checkout, responsive layouts, and mobile usability.

Platforms covered

A repeatable setup matrix kept checks consistent from desktop browsers to mobile Safari.

ChromeWindows 11
EdgeWindows 11
iPhone 10iOS Safari
iPhone 14iOS Safari
iPhone 15iOS 17

Findings & outcomes

iPhone · UX

Checkout button fell below the initial viewport on iPhone 10. Documented with screenshot evidence.

Edge · Layout

Product carousel arrows overlapped the price label in Edge, while the same layout worked in Chrome.

iOS · Forms

Search input auto-zoom shifted the layout on iPhone 14 and 15 and did not snap back after focus.

Chrome · Pass

Browse, add to cart, checkout, and order confirmation all worked as expected on Windows 11.

05Education & certifications

Grounded in learning.

Formal training and continued study supporting a practical, evidence-led approach to quality.

Certifications

Certified Tester Foundation Level (CTFL)ISTQB
AWS Certified Cloud PractitionerAmazon Web Services
Manual Testing with BrowserStackBrowserStack
Certified Network Security SpecialistCNSS
VMware VCA-DBTVMware

Education

M.S. Information Technology (in progress)Western Governors University
B.S. Technical ManagementDeVry University · 2023
06Get in touch

Let’s make good
software better.

Open to remote Manual QA Tester roles and thoughtful conversations about product quality.